
100% US-based
SOC
SOC 2 Type II
Certified
10+ years running a managed SOC
What does AMDR mean in cybersecurity?
AMDR stands for Agentic Managed Detection and Response. It is a managed cybersecurity service in which AI agents investigate eligible alerts, execute approved response actions, document their work, and escalate decisions that require human judgment.
AMDR combines the ongoing monitoring, investigation, and response of traditional MDR with agents that can carry out multiple steps of a security case. The aim is to move from an alert to an investigated, resolved, and explained outcome with less repetitive manual work.
In BitLyft’s model, BitLyft AIR® handles routine investigation and response within policy, while a human-led, 100% U.S.-based security operations center (SOC) owns high-risk calls. It is a managed security operation, not just another tool for your team to operate.
How does AMDR work?
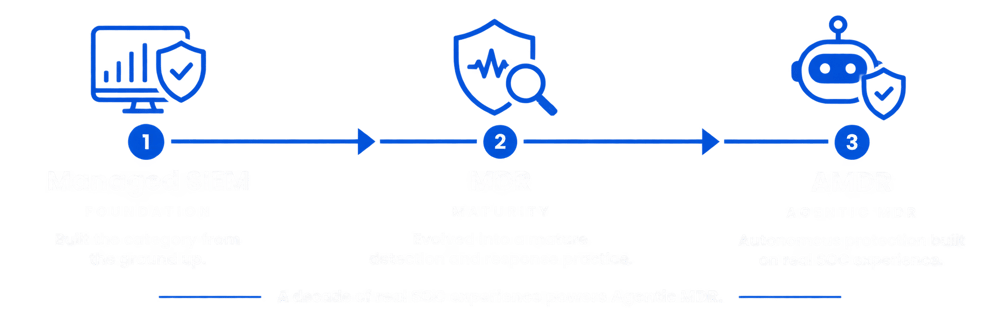
In cybersecurity, agentic means working toward a defined objective across several steps. An agent can gather evidence, connect signals, evaluate a playbook, and take an approved action instead of only generating an alert or suggesting what a person should do next.
-
Watch the environment
Monitor signals across connected endpoint, network, cloud, identity, and productivity systems.
-
Investigate the activity
Gather context, correlate related signals, and assess whether the activity represents a threat.
-
Decide within policy
Evaluate the evidence against approved playbooks, risk tolerance, and confidence thresholds.
-
Respond to eligible cases
Execute permitted containment or remediation actions. Route actions that exceed authority to a human analyst.
-
Document the outcome
Record the evidence, reasoning, actions, and result so the security team can review what happened and why.
-
Escalate when needed
Give the SOC an assembled investigation when a case is high-risk, ambiguous, or outside approved policy.
The difference is the scope of the work: task automation performs a predefined action; an agentic workflow can investigate and work an eligible case across multiple steps, within guardrails.
AMDR vs. MDR: what changes?
Traditional MDR combines security technology with analysts who monitor, investigate, and respond to threats. Many MDR services already use automation. AMDR extends that model by giving agents a larger role in completing eligible investigations and response workflows.
| Capability | Traditional MDR | AMDR |
|---|---|---|
| Monitoring | Continuous monitoring across supported systems | Continuous monitoring across supported systems |
| Investigation | Primarily analyst-led, often supported by automation | Agent-led for eligible routine cases, with SOC oversight |
| Response | Analyst action or predefined automation | Approved agentic actions, with humans owning high-risk decisions |
| Case records | Analyst notes, evidence, and reports | Evidence, reasoning, actions, confidence, and outcome |
| Escalation | Analysts investigate and determine next steps | Agents assemble context; the SOC decides when risk or authority requires it |
AMDR is not “MDR without people.” The operating model changes, but human accountability remains essential. Exact capabilities depend on the provider and your environment.
What can AMDR help investigate and resolve?
Coverage depends on connected systems, approved playbooks, and the organization’s risk tolerance. Common use cases include:
Identity and account compromise
Investigating suspicious sign-ins, compromised accounts, and unusual privilege changes.
Phishing and business email compromise
Examining malicious messages, attacker-created forwarding rules, and affected accounts.
Endpoint threats and malware
Investigating endpoint activity and containing eligible threats through approved actions.
Early ransomware activity
Connecting warning signs and supporting containment of suspicious activity or lateral movement.
Insider threats and privilege misuse
Flagging risky administrative activity and changes that need closer investigation.
Cloud and SaaS configuration risk
Examining risky application grants, identity drift, and changes to MFA policies.
Does AMDR replace security analysts?
No. It changes where analysts spend their time. Agents take on repetitive, policy-defined work so people can focus on exceptions, ambiguous activity, business context, and decisions with significant consequences.
A team without its own SOC can use AMDR as a managed security operation. An established security team can use it to extend coverage and reduce routine investigative workload. Neither model removes the need for human expertise.
Autonomy needs clear boundaries.
Before choosing a service, ask:
- Which actions can run automatically, and which require approval?
- What evidence and reasoning can our team review?
- How are actions, outcomes, and exceptions recorded?
- When does a case reach a human, and who owns the decision?
Visible evidence and clear escalation rules make the operation easier to review, govern, and explain to leadership and auditors.
Who is AMDR for?
AMDR can suit mid-market organizations that need continuous security coverage without building and staffing an entire SOC. It is relevant to CISOs and IT leaders managing growing alert volumes, limited analyst capacity, and a complex technology stack.
Banking, utilities, healthcare, higher education, manufacturing, and aerospace teams may all have this need. Regulated organizations should evaluate the specific service, data handling, response controls, and compliance requirements. For defense-industrial-base and CMMC programs, review BitLyft’s MDR for CMMC offering separately.
How BitLyft delivers AMDR
BitLyft Agentic MDR combines BitLyft AIR® with a 100% U.S.-based SOC, threat hunting, detection engineering, response, and reporting. AIR investigates and resolves eligible routine activity, while the SOC remains accountable for high-risk decisions.
BitLyft supports more than 200 integrations across identity, endpoint, cloud, and productivity tools. Deployment is shaped around your environment: the connected data, the activity to watch, the approved actions, and the playbooks that fit your risk tolerance.
The distinction is straightforward: AIR is the autonomous SOC technology; AMDR is the managed service in which BitLyft operates that technology for you.
Frequently asked questions about AMDR
What does AMDR stand for?
In cybersecurity, AMDR stands for Agentic Managed Detection and Response. It combines managed security operations with AI agents that investigate and resolve eligible routine cases within policy, while human analysts remain accountable for high-risk decisions.
Is AMDR the same as MDR?
AMDR includes the core purpose of MDR: monitoring, detection, investigation, and response. It adds agents that can carry out eligible investigation and response workflows. It evolves the operating model without removing human accountability.
Is AMDR fully autonomous?
Not without limits. Routine activity can be handled within approved policies, but high-risk, ambiguous, or out-of-policy decisions require human oversight. The scope depends on integrations, playbooks, and the organization’s risk tolerance.
Does AMDR replace a SOC?
AMDR can provide a managed security operation for an organization without its own SOC, or augment an existing team. It does not eliminate the need for human security expertise.
What threats can AMDR address?
Depending on coverage and approved actions, AMDR can support investigation and containment of identity compromise, phishing and business email compromise, endpoint malware, ransomware signals, insider risk, and cloud or SaaS misconfiguration.
How is AMDR different from an AI-native SOC tool?
An AI-native SOC tool is software your team operates. AMDR is a managed service in which a provider operates the technology and supplies a human-led SOC accountable for investigation, escalation, and response decisions.
See AMDR in your environment
Explore how agent-led investigation and accountable human oversight could fit your team, tools, and response policies.
Request a Demo