
 By
·
5 minute read
A business's security operations center (SOC) is a business unit that contains all of a company's security personnel. These highly trained cybersecurity professionals monitor networks, inform organizational leaders of potential threats, address vulnerabilities, prioritize security operations, and respond to cyberattacks. While a SOC is an essential part of maintaining network security, it has a critical drawback. Maintaining an on-premise SOC is expensive. It requires the annual salary of highly trained cybersecurity professionals, infrastructure, and software required to protect your network.

As businesses consider these expenses along with the issues of a widening talent gap in the cybersecurity sector, many turn to SOC as a Service companies for a solution. SOC as a Service (SOCaaS) is a service provided by an external that manages your internal security in the same way as an on-prem SOC. SOCaaS providers use software and cloud-based services along with support from an experienced team of cybersecurity professionals to provide 24/7 protection against modern cyberthreats. If you're unfamiliar with SOCaaS, these articles can help you learn more about the services they provide.
- What Are SOC as a Service (SOCaaS) Companies?
- SOC as a Service: What You Need to Know
- SOC as a Service: Outsourced SOC
- SOC as a Service Improves Security in Higher Ed
Clearly, SOCaaS companies can provide value to companies of any size across all industries in today's expansive threat landscape. Still, it can be difficult to know where to start when deciding which company is right for you. This list offers a comparison of the top SOC as a Service companies and profiles the most important features of the services they offer.
BitLyft Cybersecurity
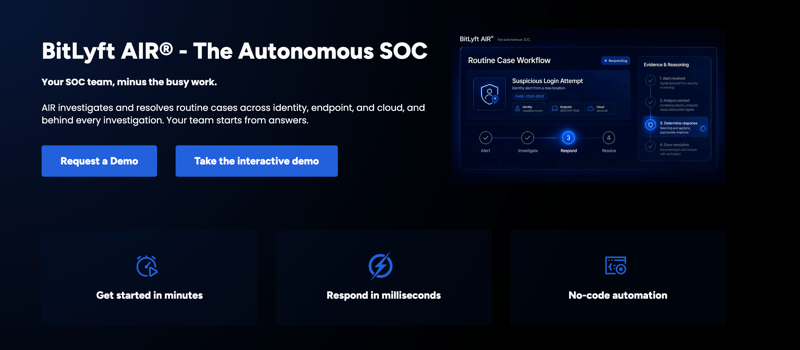
BitLyft AIR® is an AI SOC platform that detects, investigates, and resolves routine security cases on its own, then brings in a person whenever a situation genuinely calls for human judgment. Instead of handing your team a queue of alerts to work through, AIR closes cases and shows its work, with a confidence score and full reasoning for every action it takes.
It is backed by more than a decade of hands-on SOC experience and a US-based team. That gives mid-market organizations a way to get the speed of AI without giving up the people who know their environment.
Key Features
- AI agents that handle detection, investigation, and response for routine cases
- Resolution with shown work: a confidence score and full reasoning behind every action
- Human escalation built in, with US-based analysts who step in when judgment is needed
- Flexible deployment: run it with your own team, or hand it to ours
- Integrations across the tools you already run, including Microsoft 365, AWS, Google Workspace, Aurora, Rapid 7, Crowdstrike, OneLogin and more.
- Compliance support, including SOC 2 Type II certification, NIST 800-171 alignment, and GovCloud hosting availability
Pros & Cons
Reviews from Gartner Peer Insights note these pros and cons for BitLyft.
Pros
- Resolves routine cases on its own, so alert triage and investigation stop eating your team's day
- Shows its work, with a confidence score and full reasoning behind every action
- Flexible deployment: run it yourself, split the work in a partially managed model, or hand it to BitLyft's US-based SOC
- Works alongside your existing tools and your MSP instead of replacing them
- Compliance support, including SOC 2 Type II certification and NIST 800-171 alignment
- Built for lean teams that need 24/7 coverage without building a full SOC
Recommended for
BitLyft AIR® is built for mid-market organizations that don't have a full security team, and it works just as well for teams that want to run it themselves. You can hand the work to BitLyft's US-based SOC, run AIR on your own, or split it in a partially managed model that includes working alongside your MSP.
Whichever way you deploy it, AIR gives your team back time. It takes on the alert triage and case investigation that eat up the day, so your people can focus on the work that needs them.
Price Range
BitLyft AIR® pricing depends on your environment and how much of the work you want BitLyft to run. See the pricing page for how the options compare, or request a demo to talk through what fits your team.
Arctic Wolf
Arctic Wolf offers Aurora® Managed Detection and Response, powered by its Aurora Agentic SOC. The company says AI agents work alongside its Concierge Security Team, with humans keeping decision-making authority. Coverage spans endpoints, network, cloud, and identity through an open XDR architecture
Key Features
- 24/7 monitoring and security investigations
- Agentic SOC
- Concierge Security Team
- Open XDR
Pros & Cons
Reviews from Gartner Peer Insights noted these pros and cons of Arctic Wolf managed services.
Pros
- 24/7 monitoring, including outside business hours
- Broad coverage
- Incident response support included
Cons
- Some alerts lack clear remediation guidance
- Some alerts duplicate notifications from Microsoft
- Gaps with certain security tools
- Warranty is tied to optional three-year terms, and pricing requires a sales conversation
Recommended for
Arctic Wolf targets mid-market and enterprise organizations in financial services, healthcare, manufacturing, legal, and government.
Price Range
Arctic Wolf sells through Security Operations Bundles and shares pricing through a sales conversation.
Rapid7
Rapid7's SOC as a Service offering is Managed Threat Complete, a 24x7 MDR service that includes threat hunting, containment, and expert guidance. Rapid7 is building agentic AI into the service to speed up alert triage and investigation, with analysts making the final calls.
Key Features
- 24x7 managed detection and response with threat hunting and containment
- AI-enhanced triage and investigation
- Dedicated cybersecurity advisor
- Breach protection warranty
Pros & Cons
Reviews from Gartner Peer Insights noted these pros and cons for Rapid7.
Pros
- High-fidelity alert triage with fewer false positives
- SOC analysts work as an extension of your team
- Detailed incident reports with attack timelines and remediation steps
Cons
- Limited transparency into why incidents were closed
- Not enough explanation or context from the SOC team
- Little documentation to learn from investigations
- Vulnerability, application security, and other services are separate offerings
Recommended for
Rapid7 offers MDR for Microsoft and MDR for Enterprise alongside its standard service. It fits organizations that want MDR tied to exposure management and a SIEM-based platform.
Price Range
Rapid7 pricing is quoted based on the number of assets in your environment, with unlimited ingestion and long-term retention.
CrowdStrike
CrowdStrike's SOC as a Service offering is Falcon Complete Next-Gen MDR, a 24/7 expert-led, AI-accelerated service where CrowdStrike's analysts monitor, investigate, and respond on your behalf. It runs on the Falcon platform.
Key Features
- 24/7 expert-led monitoring, investigation, and response
- AI-accelerated detection and triage
- Hands-on threat response, not just alerting
- Built-in threat intelligence
Pros & Cons
Reviews from Gartner Peer Insights noted these pros and cons for CrowdStrike Security Services.
Pros
- Team of experienced analysts investigating and responding around the clock
- Built-in threat intelligence helps reduce false positives
- Fast response times from one integrated team
Cons
- Positioned toward enterprise organizations
- Managed service is built around the Falcon platform
- One reviewer said sales promises did not match the delivered experience
Recommended for
CrowdStrike positions its SOC offerings toward enterprise organizations. Falcon Complete fits teams already running the Falcon platform.
Price Range
Crowdstrike offers four pricing packages that cover its entire service lineup.
-
CrowdStrike lists per-device prices for its endpoint bundles, billed annually:
- Falcon Go: $59.99 per device (limited to 100 devices)
- Falcon Pro: $99.99 per device
- Falcon Enterprise: $184.99 per device
Ready to See an AI SOC in Action?
SOC as a Service gives organizations access to experienced security teams without the cost of building a SOC in-house. As AI takes over the routine work, the strongest options combine automation that closes cases with people who step in when it matters.
That is what BitLyft AIR® was built to do. See how it investigates and resolves real cases, with the reasoning shown, and find out what it would look like in your environment.